


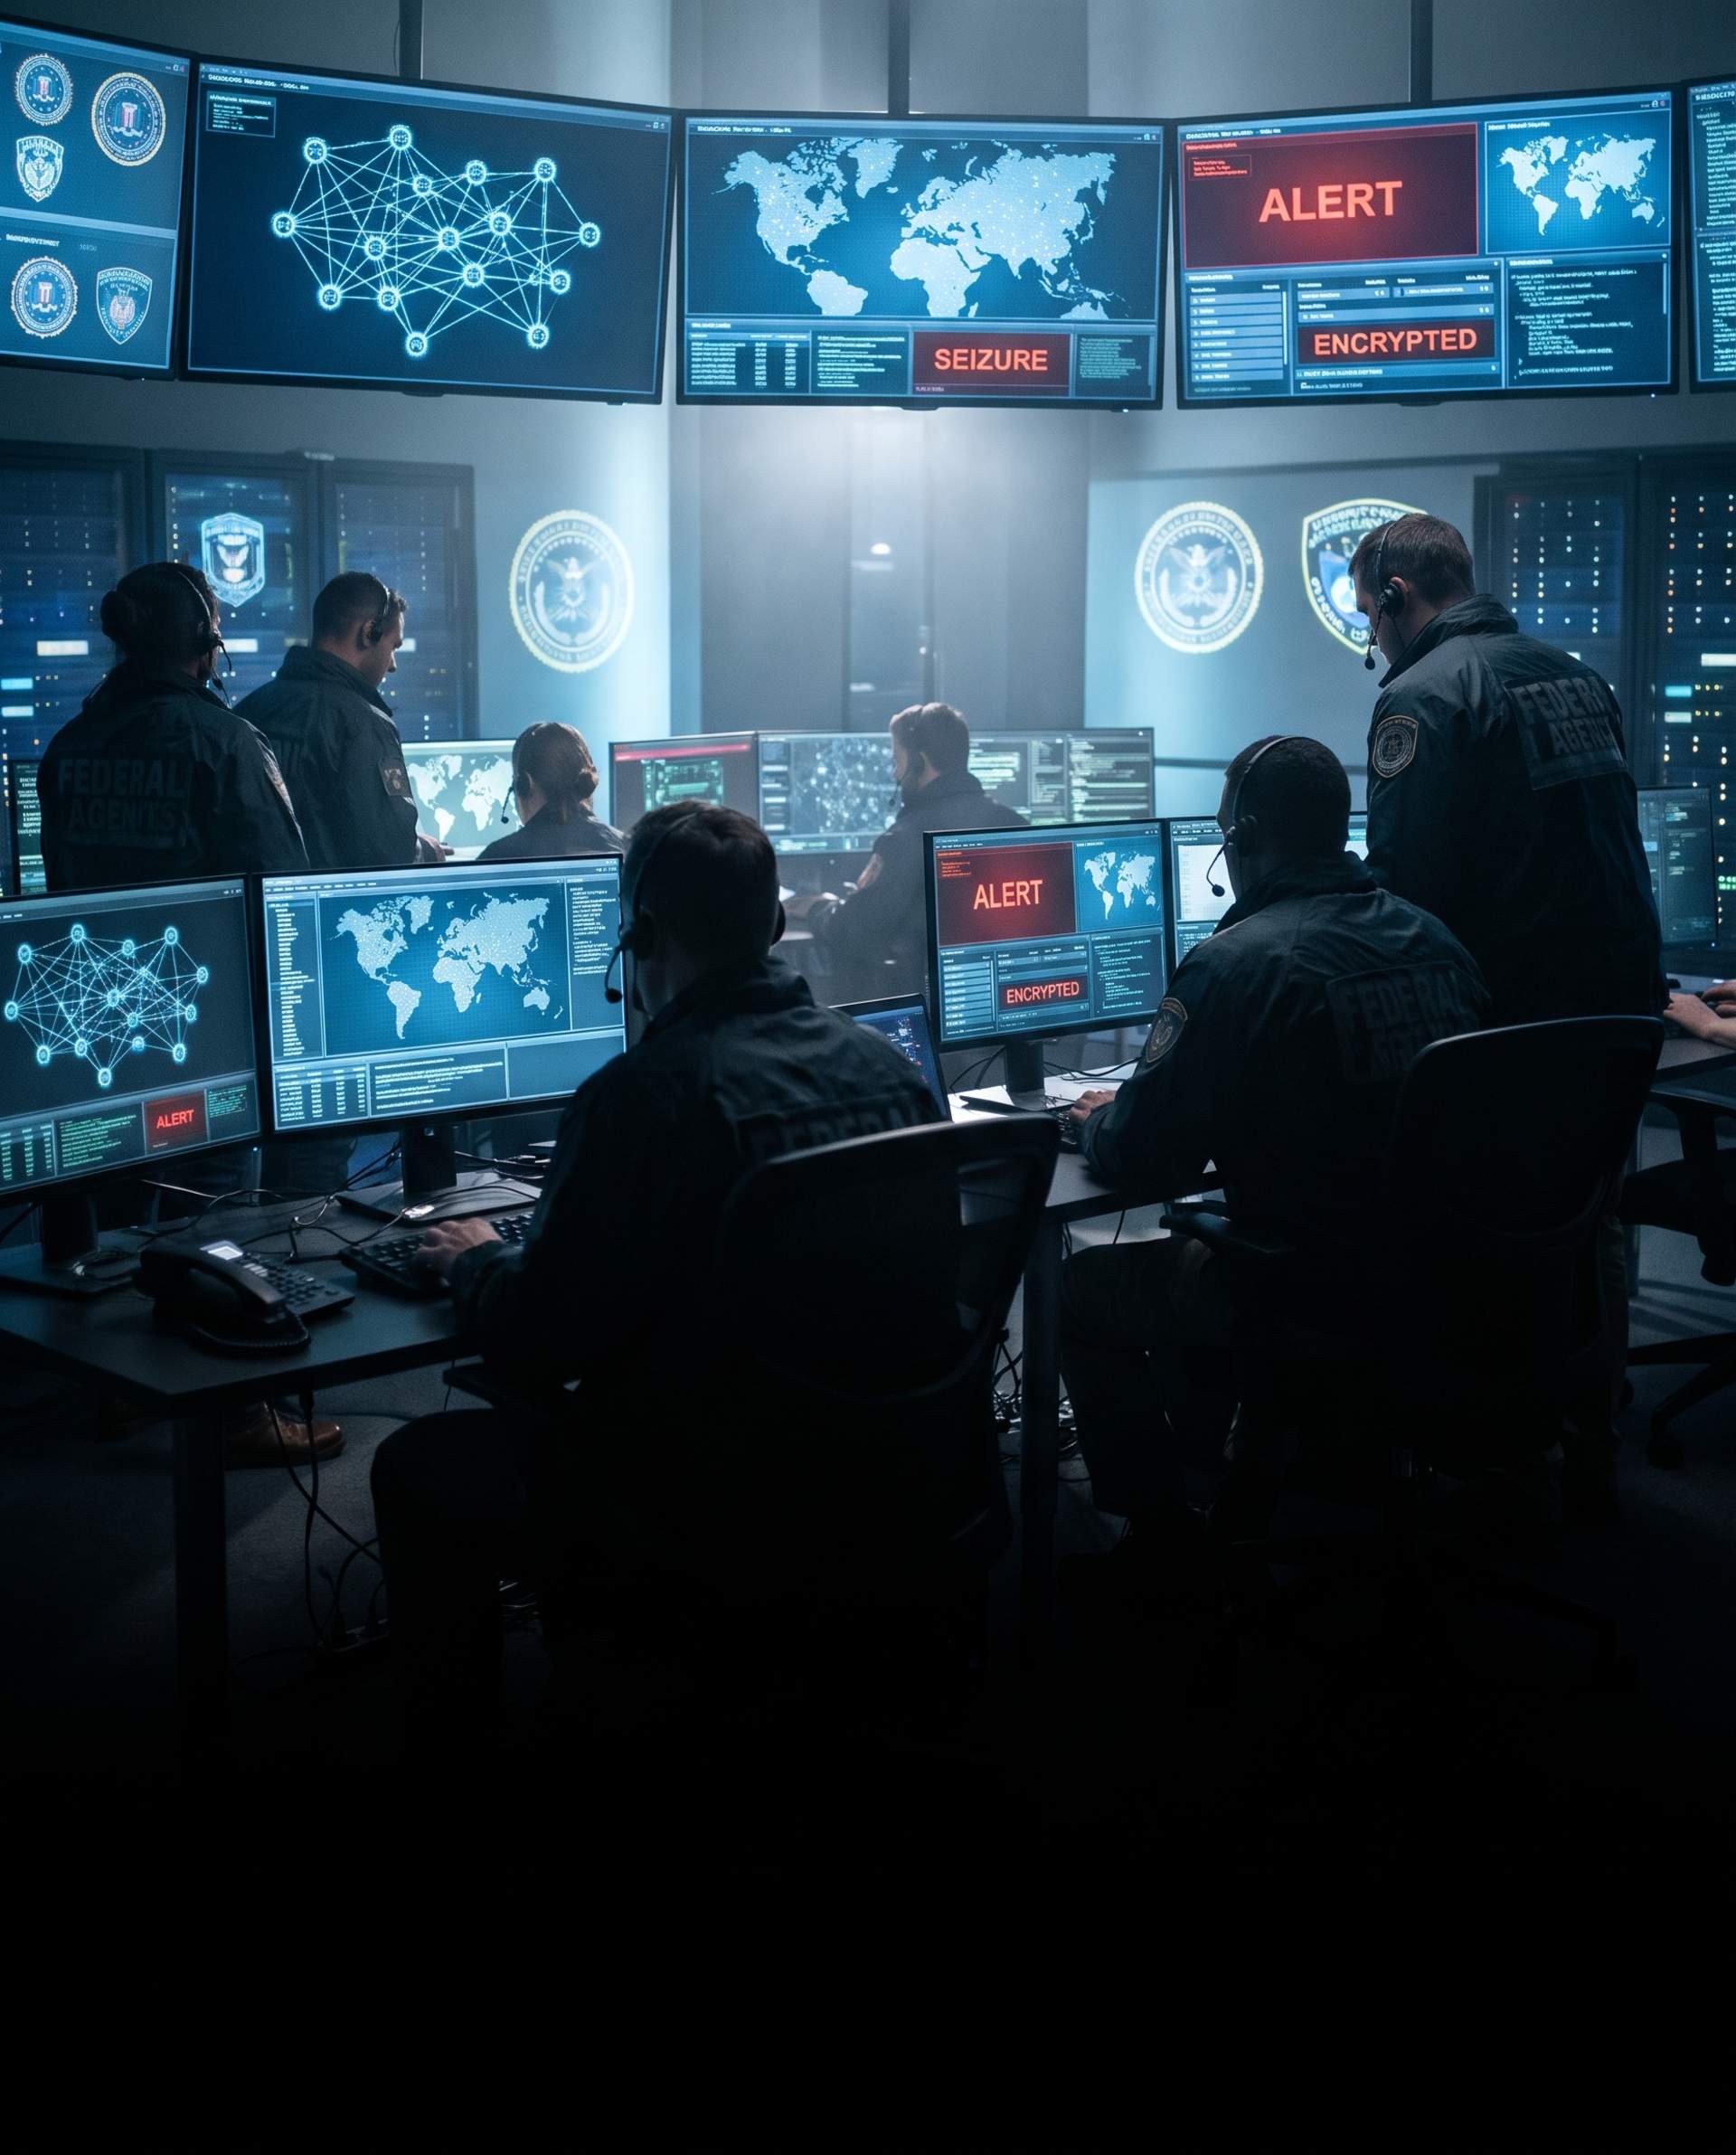
In one of the most successful international law enforcement operations against transnational cyber extortion networks to date, a coalition spanning thirteen countries has seized dark web infrastructure and released free master decryption keys to neutralize the notorious BlackByte ransomware syndicate.
The coordinated global strike, codenamed Operation Sentinel Strike, was orchestrated jointly by the European Cybercrime Centre at Europol, the United States Federal Bureau of Investigation, and specialized cybersecurity agencies across Europe and Asia. Over forty command-and-control servers, cryptocurrency wallet ledgers, and illicit communication channels scattered across hosting providers in four continents were seized simultaneously, bringing an abrupt halt to an extortion group that has extracted hundreds of millions of dollars from victims worldwide.
A Relentless Threat to Critical Infrastructure
First detected by threat intelligence researchers in late 2021, the BlackByte ransomware group quickly established itself as one of the most predatory ransomware-as-a-service enterprises in cyberspace. Unlike some opportunistic attackers that focus on individual consumers, BlackByte specifically targeted critical infrastructure sectors, including municipal utility networks, healthcare providers, educational institutions, and financial manufacturing conglomerates.
The syndicate operated through a double-extortion business model. Affiliates would infiltrate corporate local area networks using unpatched edge vulnerabilities and compromised administrator credentials. Once inside, they spent weeks covertly moving across network subnets, exfiltrating terabytes of confidential business files and patient records to external servers before detonating sophisticated encryption payloads that brought critical operational systems to a standstill.
Victims who refused to pay multimillion-dollar ransoms in untraceable cryptocurrencies saw their sensitive intellectual property and employee personal data dumped onto public dark web shaming blogs.
Sophisticated Evasion Tactics and Driver Exploits
What made BlackByte particularly lethal was its pioneering use of bring-your-own-vulnerable-driver techniques. The malware abused legitimate, digitally signed third-party system drivers containing known security flaws to bypass modern endpoint detection and response software.
By executing with kernel-level operating system privileges, the ransomware would systematically blind antivirus defenses, disable volume shadow copies, and terminate system monitoring services before initiating file encryption. Cybersecurity defense teams across the globe are already incorporating the technical indicators of compromise extracted during the police raid into commercial firewall signatures, insulating thousands of enterprises against related malicious loader families.
Covert Infiltration and the Master Decryptor
The takedown represents the culmination of more than sixteen months of covert investigative work by specialized cyber forensic investigators. Law enforcement personnel successfully breached BlackByte's internal communication networks and source code repositories, gaining administrative visibility into how the syndicate distributed cryptographic keys.
Crucially, cyber forensic analysts from the Dutch National Police discovered a critical flaw in the ransomware's pseudo-random number generator implementation. Investigators quietly harvested the master mathematical seed pairs used by BlackByte's encryption engine across hundreds of enterprise infections. Working alongside the No More Ransom project, Europol has released a free public decryption tool that allows affected organizations to recover their locked files without handing over a single dollar in extortion payments.
Tracking Illicit Cryptocurrency Laundering Chains
In addition to dismantling physical server infrastructure, financial intelligence investigators delivered a severe blow to the criminal organization's banking pipeline. By tracing complex cryptocurrency peeling chains across privacy-focused mixing services and decentralized crypto exchanges, authorities froze over thirty million dollars in digital assets linked directly to syndicate leaders.
Financial analysts revealed that the group utilized complex multi-layered transactions across jurisdictions in Eastern Europe and Central America to convert extortion proceeds into luxury real estate and physical gold bullion. Multiple arrest warrants and Interpol red notices have been issued against core developers and money laundering facilitators suspected of running the technical operations.
Strengthening Global Defenses Against Future Threats
While the elimination of BlackByte marks a momentous victory for global digital resilience, cybersecurity authorities caution that corporate defenses must remain vigilant. Takedowns of high-profile cybercrime cartels often trigger splinter groups, where displaced developers reassemble under new operational pseudonyms with rewritten malicious codebases.
Government cyber agencies are urging private enterprises and critical infrastructure operators to accelerate zero-trust network architectures, enforce mandatory hardware-based multi-factor authentication, and isolate administrative backup systems from general office networks. As the digital domain remains a contested frontier, sustained international police coordination and transparent intelligence sharing between public and private sectors remain the most effective weapons against modern cybercrime syndicates.
Comments
0