


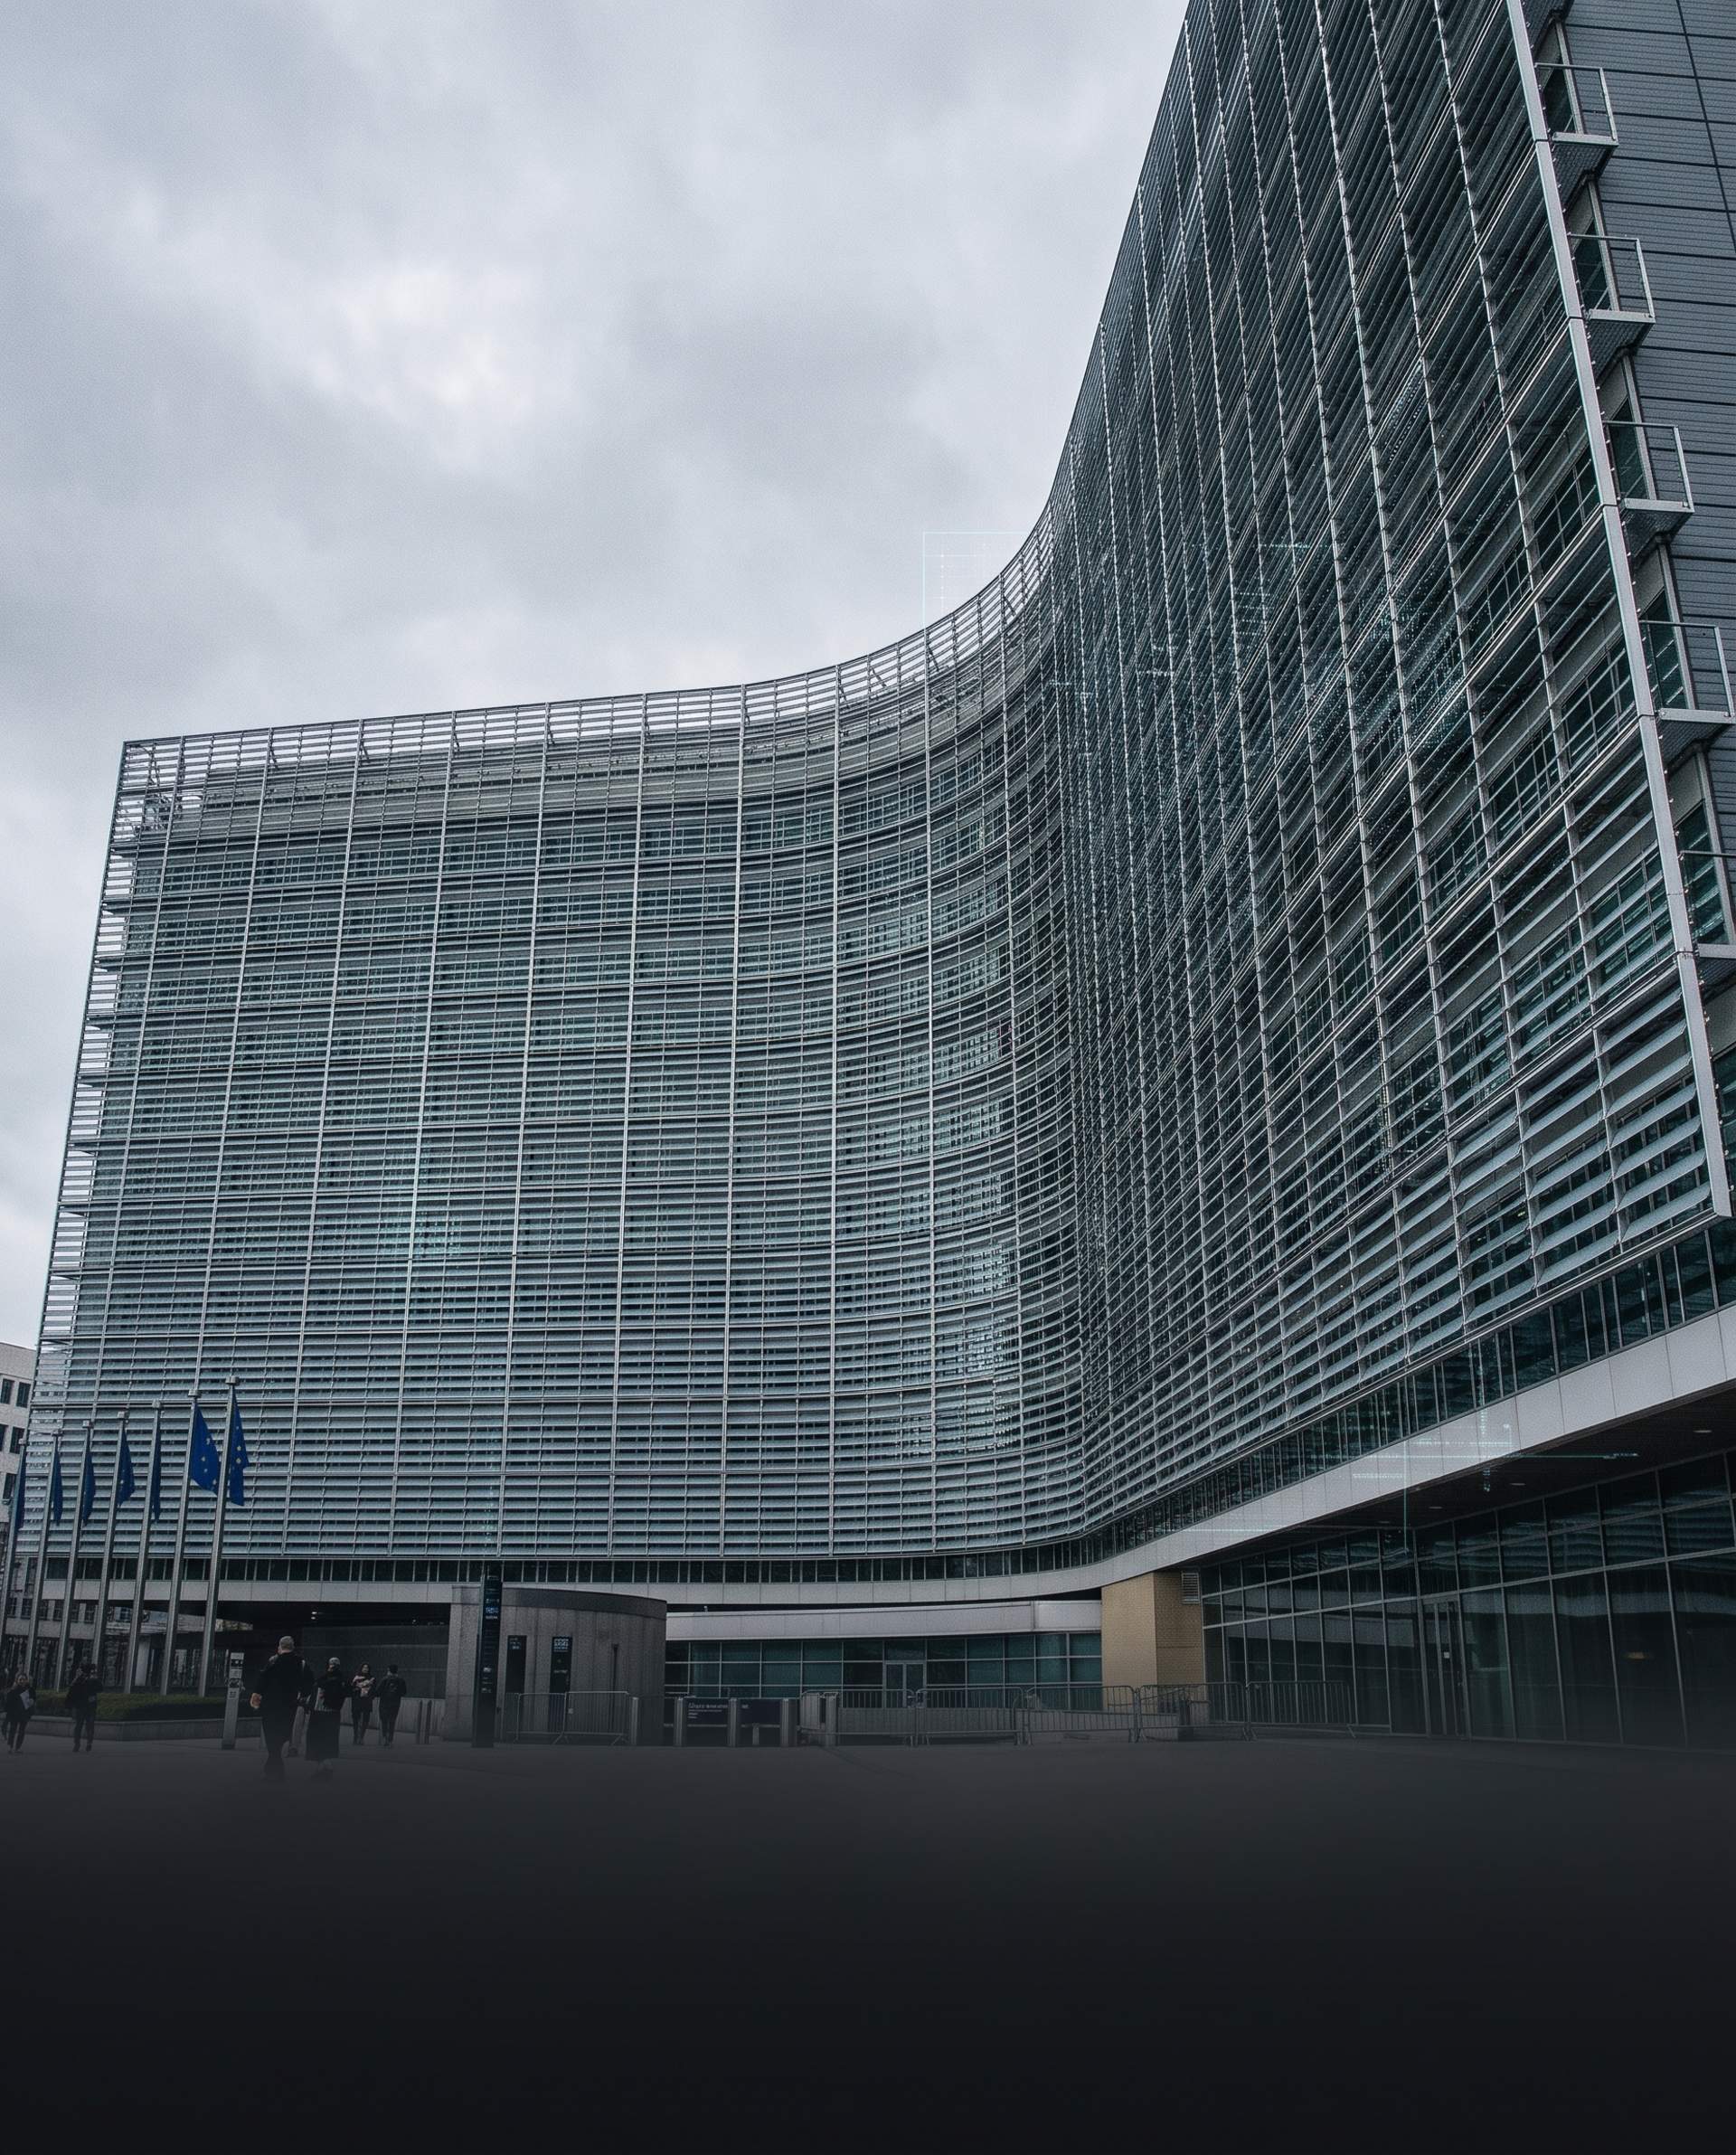
The European Commission launched formal, legally binding audits this week against top artificial intelligence companies and tech platforms under its Digital Services Act. The move sets a tough new standard for how governments police advanced software.
The enforcement action, announced in Brussels, requires companies behind frontier AI systems and autonomous agents to hand over detailed technical proof. Regulators want to inspect safety testing records, internal red-team attack reports, content filtering systems, and tools used to watermark generated media.
Using Platform Rules to Regulate Frontier Tech
While the European Union already passed its broader Artificial Intelligence Act, regulators are not waiting for its long-term rules to kick in. Instead, they are using the Digital Services Act, known as the DSA, which is already active and carries immediate legal teeth.
Under the DSA, any online platform or search engine with over 45 million monthly users in the EU must prove it is managing systemic risks to society. Those risks cover a wide range of problems, including automated disinformation networks, deepfake identity scams, automated hacking tools, and mass copyright harvesting.
European officials say the rapid rise of AI agents has made the situation much more urgent. Unlike simple chat apps, modern agents can browse the web, run terminal code, execute transactions, and tap into company databases on their own. Regulators want to ensure companies have strong guardrails in place before these tools spread across the corporate world.
What Regulators Are Demanding to See
The Commission's formal orders demand that AI builders open up their internal testing logs to European regulators and independent safety researchers. The inspection focuses on three main areas.
First, developers must show how their safety filters stop automated coding assistants from helping criminals write malicious computer viruses or generate chemical recipes. Second, companies have to prove that digital watermarking systems, such as C2PA standards, actually work to label fake photos, voices, and videos online. Third, builders must provide real data on how often their systems hallucinate or invent false facts, and what steps they take to correct those errors.
Regulators also want to inspect the audit trails for training data. They want to know whether copyrighted news articles, creative books, and private customer records were ingested without proper legal permission or compensation.
Under the DSA, failing to cooperate or providing deceptive answers can bring massive penalties. Fines can reach up to six percent of a company's total worldwide annual sales, creating huge financial pressure on Silicon Valley giants.
Industry Concerns Over Innovation and Speed
The new audits have sparked sharp debate among tech leaders. Several software developers warn that heavy paperwork and demands to reveal internal testing methods will slow down product launches and hurt European competitiveness compared to the United States and China.
Industry groups argue that vague rules around what counts as a systemic risk create confusion for software teams trying to push rapid updates. Some firms have even hinted they might delay rolling out their latest AI features in Europe to avoid legal headaches.
On the other side, consumer privacy groups and digital rights advocates welcomed the move. They argue that voluntary company pledges and self-graded report cards have consistently failed to stop online scams, deepfakes, and privacy violations during major public elections.
A Global Test Case for AI Rules
Governments in Washington, London, and Tokyo are watching Brussels closely. While many countries are still debating whether they need brand-new AI laws, the European Commission is showing that existing platform accountability statutes can be applied directly to frontier models.
European regulators will compile their findings into public reports over the next few months. If the audits uncover serious risks that companies cannot fix, the Commission has the power to order mandatory product changes, appoint independent monitors, or restrict software features across all 27 member states.
Comments
0